Location Services
This guide covers the two ways devices use nRF Cloud Location Services and what each one needs during the transition to the new nRF Cloud experience.
Which path are you on?
| How you use Location Services | What to do |
|---|---|
| Your backend calls the Location Services REST API (cloud-to-cloud) | Follow Cloud to Cloud Location Lookups to move from a service token to an OAT. |
| Your devices request their location through the nRF Connect SDK (device-to-cloud) | No token or firmware changes are required. Follow Device to Cloud Location Lookups to verify that lookups work. |
Cloud to Cloud Location Lookups
Use this section if your backend calls the Location Services REST API. You will replace a legacy service token with an organization auth token (OAT) and update your request URLs.
Service tokens and evaluation tokens are deprecated. Service tokens will continue to work during the deprecation window, but new evaluation tokens cannot be created. To avoid service disruption, complete the migration as soon as possible.
What is changing
| Aspect | Before (service or evaluation token) | After (OAT) |
|---|---|---|
| Where you get it | Legacy nRF Cloud dashboard | nRF Cloud Dashboard (via single sign-on, SSO) |
| Auth header | Authorization: Bearer <service_token> | Authorization: Bearer <OAT> |
| URL shape | /v1/location/<endpoint> | /v1/organizations/<ORG_SLUG>/projects/<PROJECT_SLUG>/location/<endpoint> |
| Scoping | Implicit per token | Scoped to a Memfault organization; project specified in the URL |
| Rotation | Manual | Manual; OATs can be revoked individually from the nRF Cloud Dashboard |
The following endpoints are also deprecated and may be removed any time after July 1, 2026:
/v1/account/service-token/v1/account/service-key-and-token
Before you begin
You will need:
- An active nRF Cloud account with the ability to log in and view the application pages described below.
- Administrator-level access on the organization you want to use Location Services. If you are not an admin, ask one of your organization's admins to either grant you the role or create the OAT for you. See Access control: teams and roles.
- Your existing API client code or device firmware so you can update the
Authorizationheader and request URL.
If you need assistance verifying any of these prerequisites,
Service tokens keep working during the deprecation window, so you can deploy OAT-based code alongside the existing token, verify it in production, and then decommission the service token. There is no need for a hard cutover.
Step 1: Log in to nRF Cloud
Go to nRF Cloud and sign in with your nRF Cloud credentials.
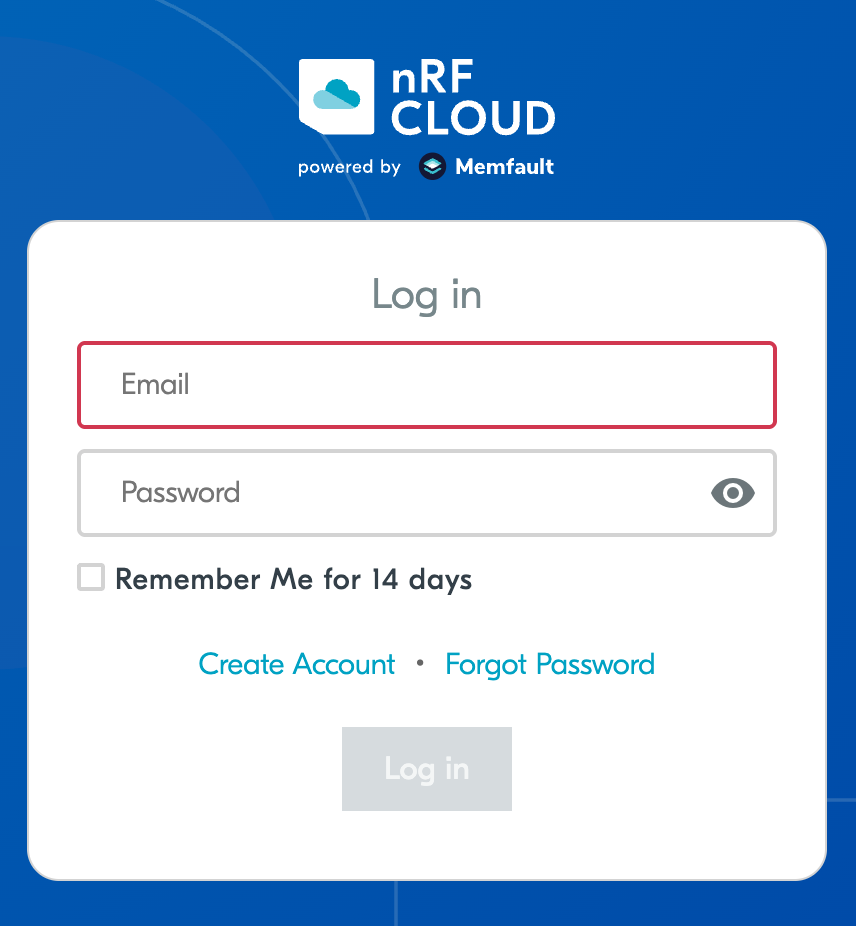
Once signed in, you land on the nRF Cloud dashboard.
Step 2: Open the nRF Cloud dashboard
This takes you to the nRF Cloud dashboard. If you are on our legacy page, please click the New Experience item on left sidebar of nRF Cloud legacy dashboard.
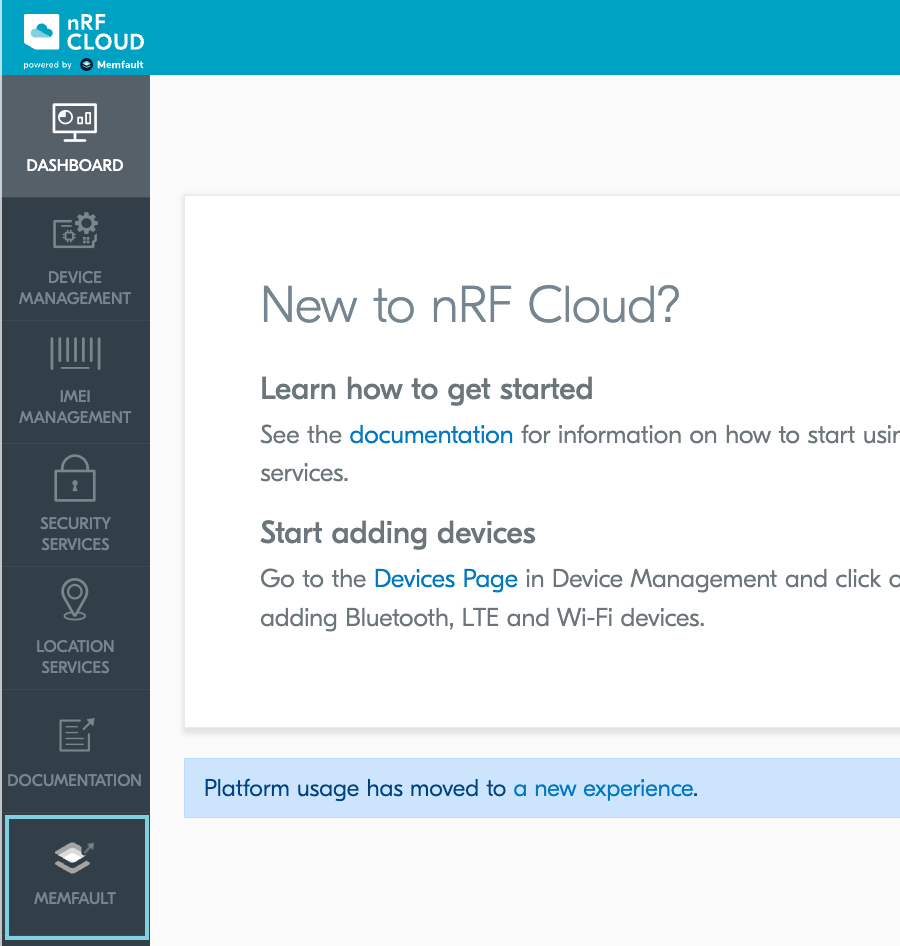
You briefly see a "Redirecting to New Experience" splash screen, then arrive at the nRF Cloud dashboard for the organization that corresponds to your nRF Cloud team.
If your nRF Cloud team was created before the nRF Cloud integration, you may see a one-time prompt to link or create an nRF Cloud organization. Accept the prompt to continue. The resulting nRF Cloud organization shares the name of your nRF Cloud team and contains a default project named nRF Project.
Step 3: Find your organization and project slugs
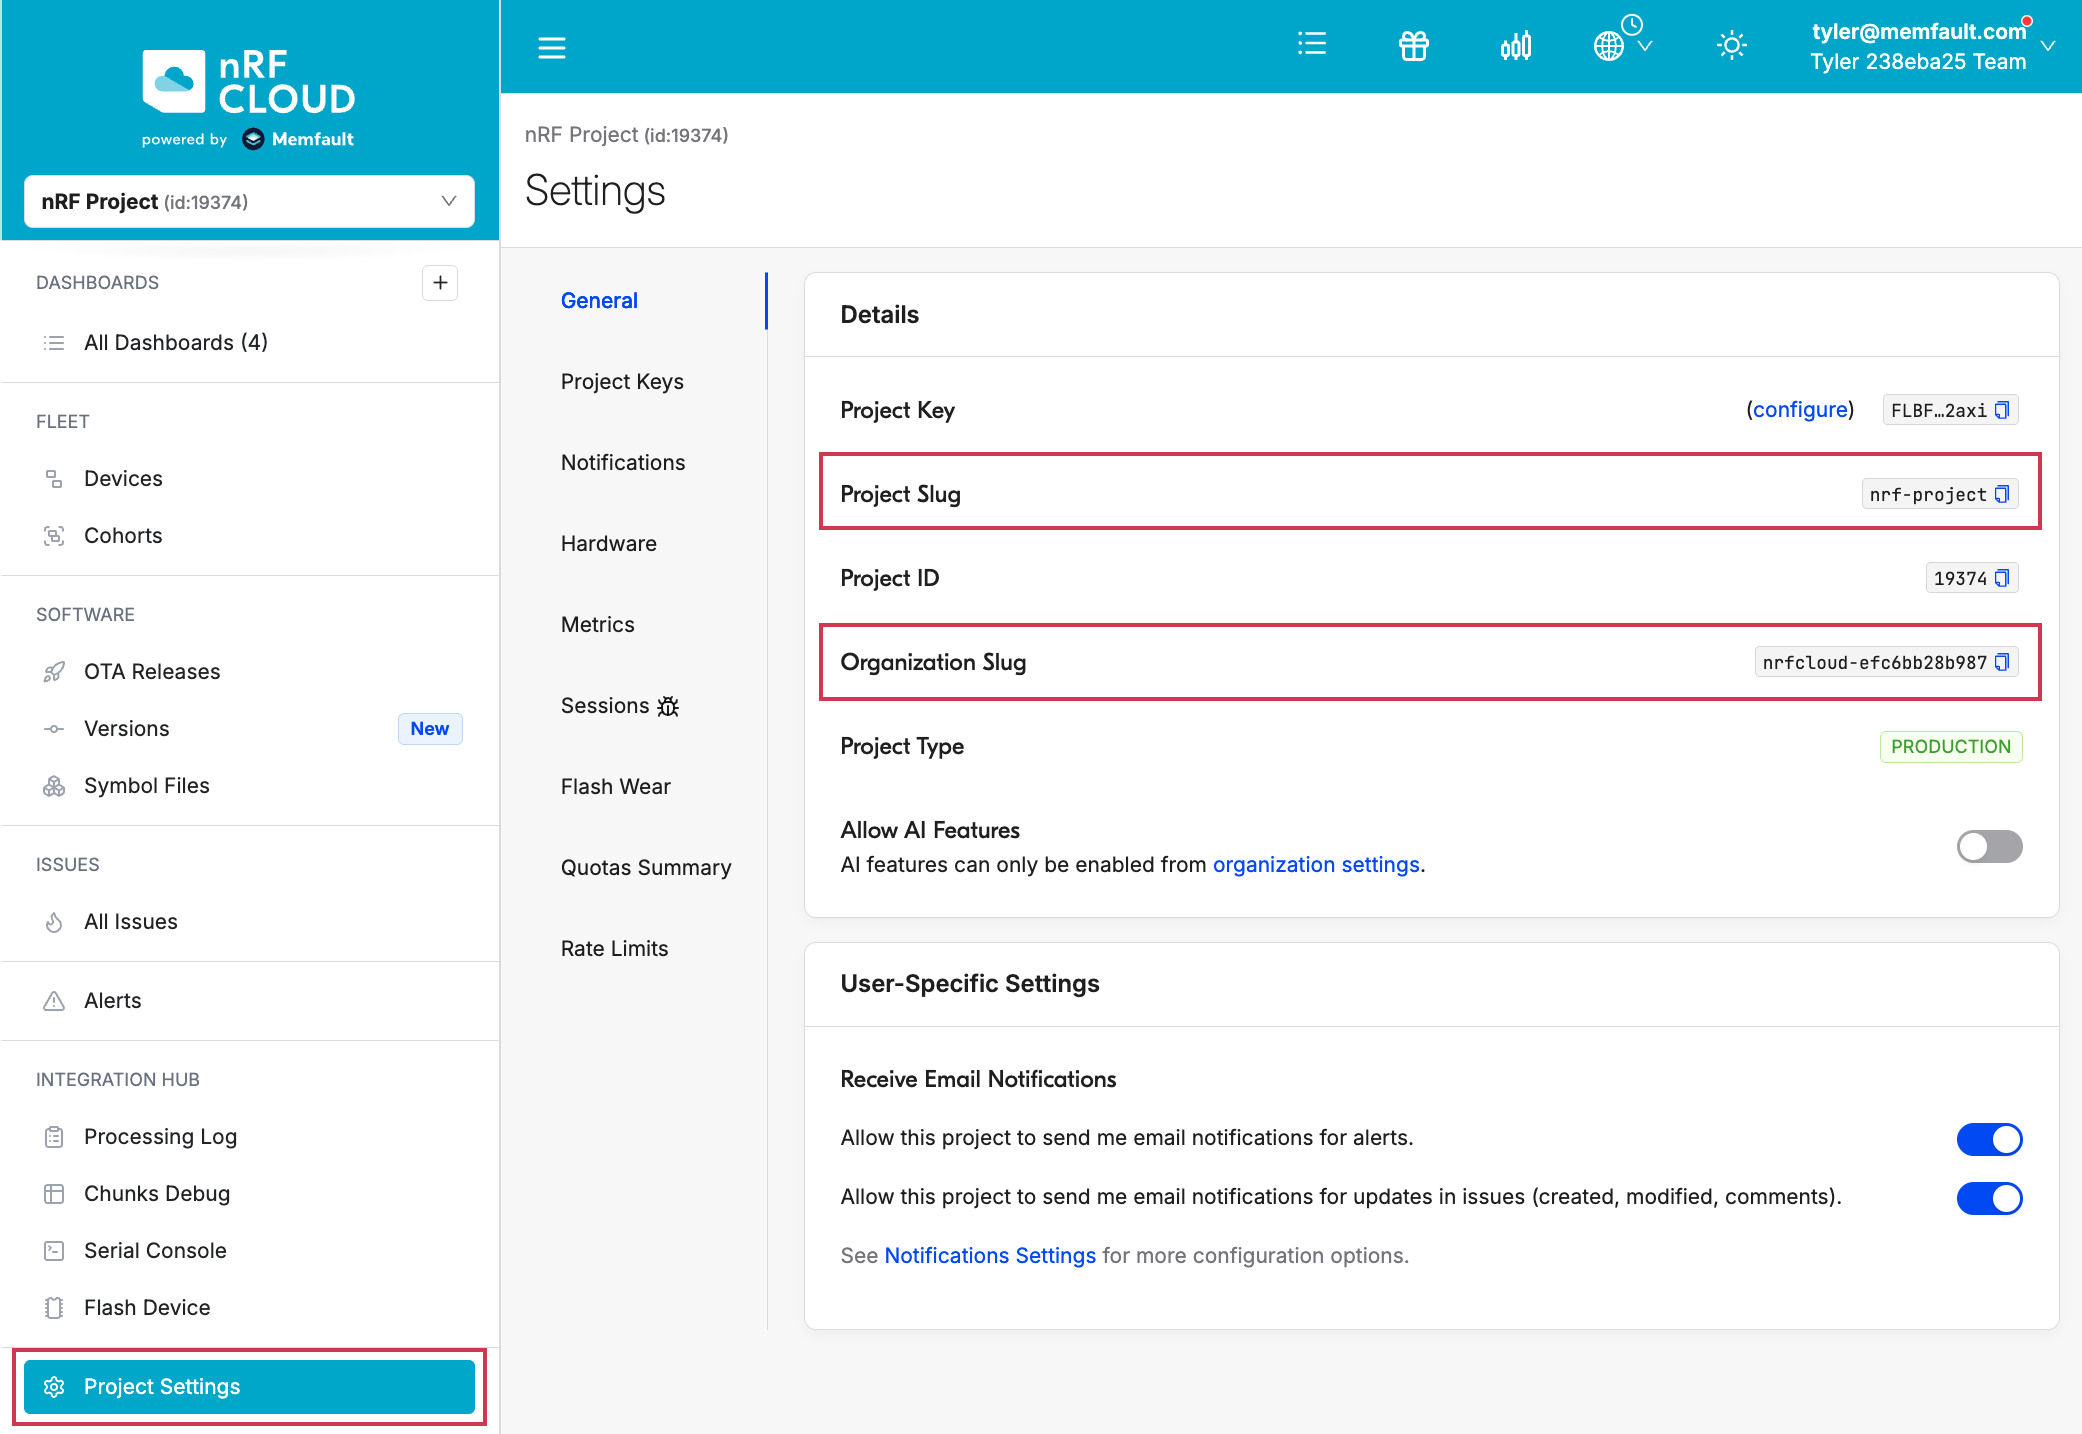
nRF Cloud structures your teams and devices in organizations and projects. You need both the organization slug and project slug to construct nRF Cloud API URLs.
In the left sidebar, click Project Settings → General. Copy the Organization Slug and Project Slug values from the Details panel.
Step 4: Create an organization auth token
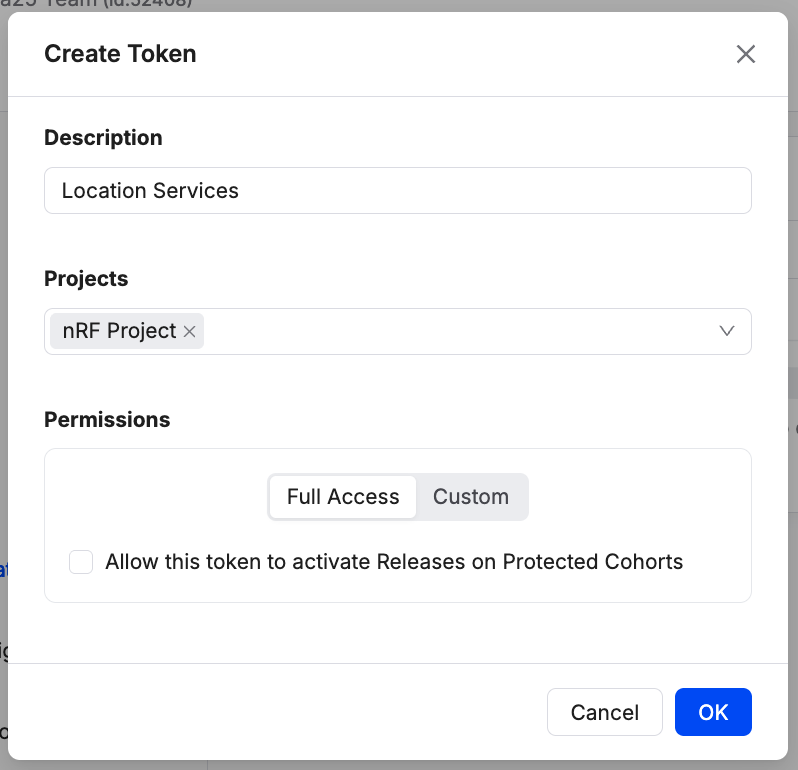
From the left sidebar, click Admin, open the Organization Auth Tokens tab, and click Create Token.
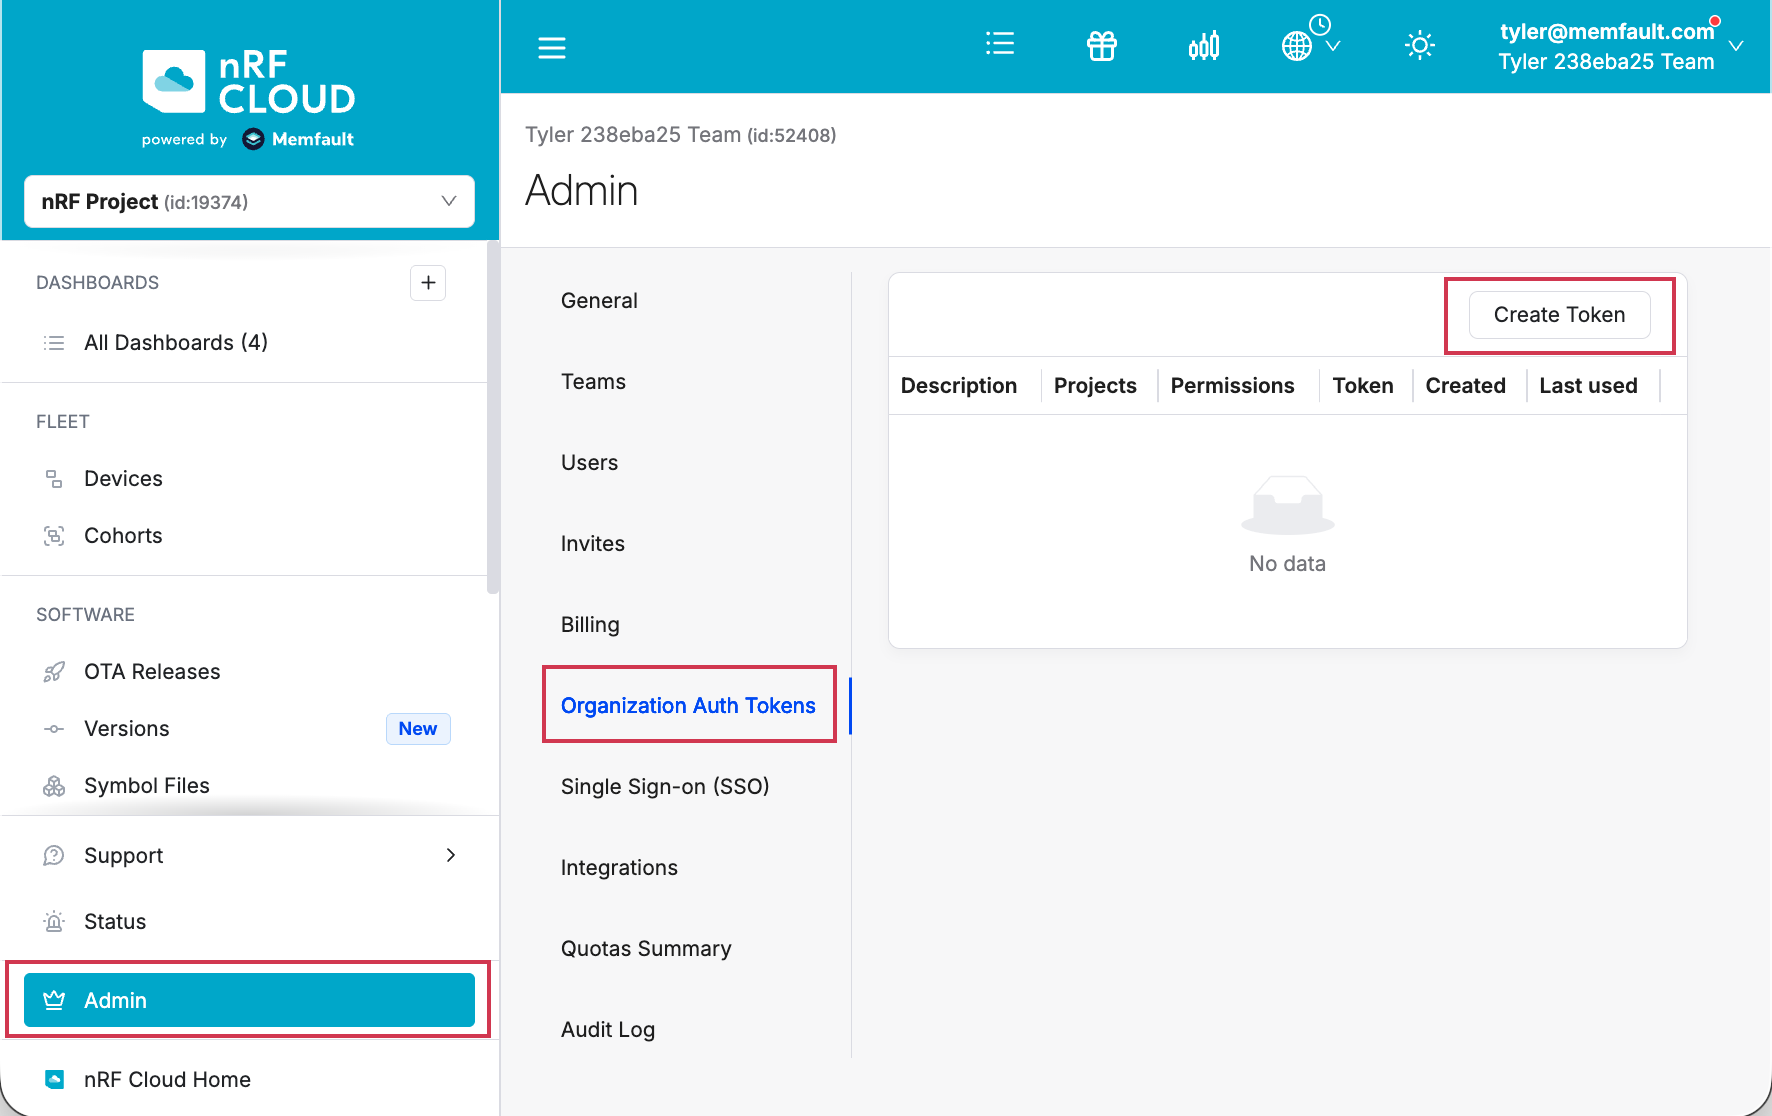
Enter a description of what the token is for (for example, Location Services
or Device onboarding) and click Create.
Copy the token immediately and store it somewhere secure. nRF Cloud does not display the secret value again.
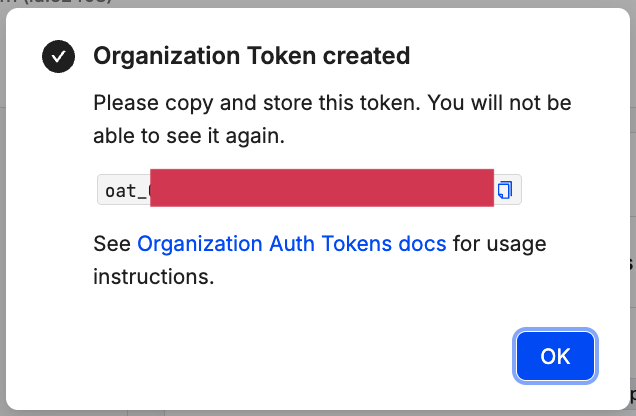
For more details on OATs, see Organization Auth Tokens.
Do not commit OATs to source control or paste them into chat. They grant the same permissions as an organization admin has via the API.
Step 5: Update your client code
You need two changes per call site:
- Replace the token in the
Authorizationheader. - Rewrite the URL to include your Organization Slug and Project Slug.
URL changes
| Endpoint | Before | After |
|---|---|---|
| Wi-Fi | https://api.nrfcloud.com/v1/location/wifi | https://api.nrfcloud.com/v1/organizations/<ORG>/projects/<PROJECT>/location/wifi |
| Cellular | https://api.nrfcloud.com/v1/location/cell | https://api.nrfcloud.com/v1/organizations/<ORG>/projects/<PROJECT>/location/cell |
| Ground Fix | https://api.nrfcloud.com/v1/location/ground-fix | https://api.nrfcloud.com/v1/organizations/<ORG>/projects/<PROJECT>/location/ground-fix |
| A-GNSS | https://api.nrfcloud.com/v1/location/agnss | https://api.nrfcloud.com/v1/organizations/<ORG>/projects/<PROJECT>/location/agnss |
| P-GPS | https://api.nrfcloud.com/v1/location/pgps | https://api.nrfcloud.com/v1/organizations/<ORG>/projects/<PROJECT>/location/pgps |
cURL example
Before: using a service token:
curl -X POST \
  https://api.nrfcloud.com/v1/location/wifi \
  -H "Authorization: Bearer $NRFCLOUD_SERVICE_TOKEN" \
  -H "Content-Type: application/json" \
  -d '{ "accessPoints": [ ... ] }'
After: using an OAT:
curl -X POST \
  https://api.nrfcloud.com/v1/organizations/$NRFCLOUD_ORG/projects/$NRFCLOUD_PROJECT/location/wifi \
  -H "Authorization: Bearer $NRFCLOUD_OAT" \
  -H "Content-Type: application/json" \
  -d '{ "accessPoints": [ ... ] }'
Step 6: Verify the new token end-to-end
Run a single request with the new URL and OAT and confirm a 200 OK:
curl -i -X POST \
  "https://api.nrfcloud.com/v1/organizations/$NRFCLOUD_ORG/projects/$NRFCLOUD_PROJECT/location/wifi" \
  -H "Authorization: Bearer $NRFCLOUD_OAT" \
  -H "Content-Type: application/json" \
  -d '{
    "accessPoints": [
      { "macAddress": "30:86:2d:c4:29:d0", "signalStrength": -45 },
      { "macAddress": "3c:37:86:5d:75:d4", "signalStrength": -45 }
    ]
  }'
If you receive a 401 Unauthorized, verify that:
- The
Authorizationheader usesBearer, notToken. - The OAT was copied in full, with no trailing whitespace.
- The Organization Slug and Project Slug match exactly what is in the nRF Cloud Dashboard (slugs are lowercase and hyphenated).
A 404 Not Found usually means the URL path is malformed. Confirm both slugs
are present and that /location/<endpoint> follows them.
Device to Cloud Location Lookups
Use this section if your devices request their location directly from nRF Cloud, for example with the Asset Tracker Template. You can confirm that lookups are working from the device page. Devices running existing nRF Connect SDK firmware continue to work with the new nRF Cloud experience without firmware updates.
-
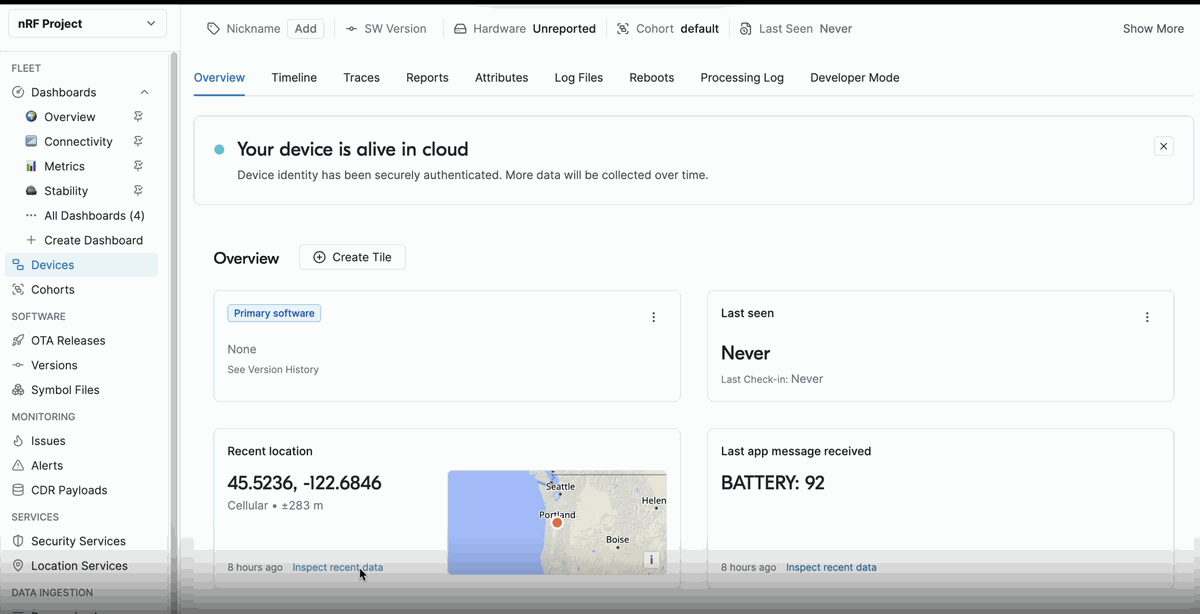
Click Devices and select your device.
-
Open the Overview tab. The Recent location tile shows the latest location report: its coordinates, source (GNSS, Cellular, or Wi-Fi), accuracy, and when it was received.
-
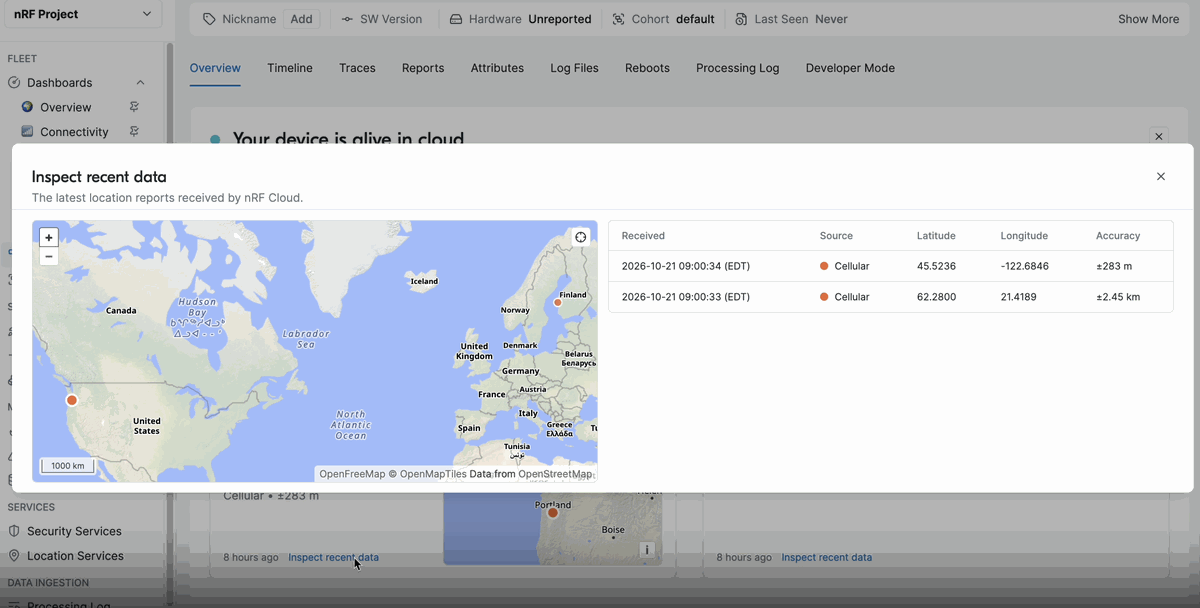
Click Inspect recent data to view the last 10 location reports on a map and in a table.
Troubleshooting
| Symptom | Likely cause | Fix |
|---|---|---|
401 Unauthorized immediately | Wrong header format, truncated token, or token belongs to a different organization | Recopy the token; confirm slugs match the org that issued the OAT |
403 Forbidden | OAT is valid but the project does not have Location Services enabled | Enable Location Services for the project, or use the project that has it enabled |
404 Not Found on a previously working endpoint | URL still uses the old /v1/location/... shape | Update to /v1/organizations/<ORG>/projects/<PROJECT>/location/... |
| No Memfault item in the nRF Cloud sidebar | Your nRF Cloud team is not yet linked to a Memfault Organization | Contact nRF Cloud support to link your team, or sign up at nRF Cloud |
| nRF Cloud Dashboard loads but Admin → Organization Auth Tokens is hidden | Your Memfault user is not an Organization Admin | Ask an admin to grant the role or create the OAT for you |